Risk Assessment Meeting
การประชุมประเมินความเสี่ยง
A team of security analysts conducts a detailed meeting to identify, analyze, and evaluate potential risks to the organization's assets. They discuss likelihood, impact, and existing controls, often using a risk matrix.
ทีมนักวิเคราะห์ความปลอดภัยประชุมกันอย่างละเอียดเพื่อระบุ วิเคราะห์ และประเมินความเสี่ยงที่อาจเกิดขึ้นกับทรัพย์สินขององค์กร พวกเขาหารือถึงโอกาสที่จะเกิด ผลกระทบ และมาตรการควบคุมที่มีอยู่ โดยมักใช้ตารางประเมินความเสี่ยง
บทสนทนา8
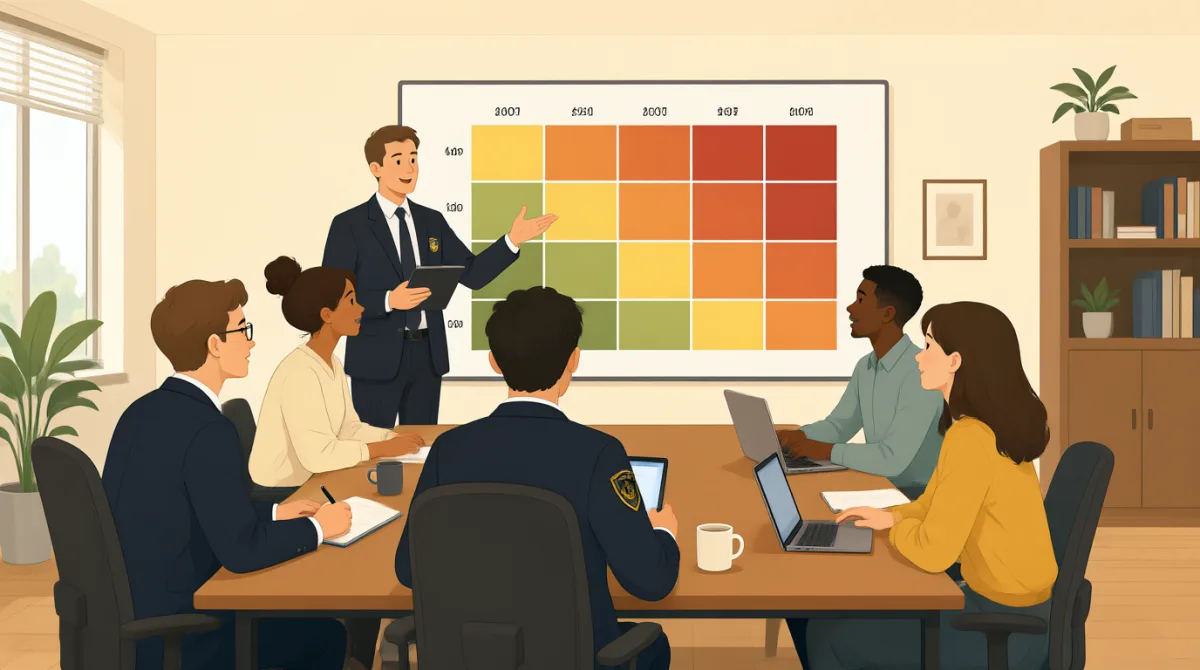

Alright team, let's kick off this risk assessment meeting. Our primary goal today is to revisit the potential vulnerabilities of our new cloud infrastructure, particularly concerning data integrity. Mia, could you start us off with your findings?
เอาละทุกคน เรามาเริ่มการประชุมประเมินความเสี่ยงกันเลย เป้าหมายหลักของเราวันนี้คือทบทวนจุดอ่อนที่อาจเกิดขึ้นในโครงสร้างพื้นฐานคลาวด์ใหม่ของเรา โดยเฉพาะเรื่องความถูกต้องครบถ้วนของข้อมูล มีอา ช่วยเริ่มนำเสนอสิ่งที่คุณพบได้ไหมครับ

Certainly, David. Based on our analysis, the most significant risk is unauthorized access leading to data corruption or loss. We're looking at a likelihood of 'moderate' and a potential impact of 'critical' if it occurs.
ได้ค่ะ เดวิด จากการวิเคราะห์ของเรา ความเสี่ยงที่สำคัญที่สุดคือการเข้าถึงโดยไม่ได้รับอนุญาต ซึ่งอาจทำให้ข้อมูลเสียหายหรือสูญหายได้ เราประเมินโอกาสที่จะเกิดไว้ที่ระดับ 'ปานกลาง' และผลกระทบที่อาจเกิดขึ้นไว้ที่ระดับ 'ร้ายแรง' ค่ะ

Moderate likelihood, critical impact… that puts it squarely in the 'high risk' category on our matrix. What existing controls do we have in place to mitigate this, Mia?
โอกาสเกิดปานกลาง ผลกระทบร้ายแรง… แบบนี้ก็จัดอยู่ในหมวด 'ความเสี่ยงสูง' ในตารางของเราอย่างชัดเจน แล้วตอนนี้เรามีมาตรการควบคุมอะไรอยู่บ้างเพื่อบรรเทาความเสี่ยงนี้ มีอา
Currently, we have robust encryption and multi-factor authentication. However, the gap identified is the lack of real-time anomaly detection within the data streams themselves, which could alert us to subtle corruption attempts.
ตอนนี้เรามีการเข้ารหัสที่รัดกุมและการยืนยันตัวตนแบบหลายปัจจัยค่ะ อย่างไรก็ตาม ช่องโหว่ที่พบคือ เรายังไม่มีระบบตรวจจับความผิดปกติแบบเรียลไทม์ภายในกระแสข้อมูลโดยตรง ซึ่งอาจช่วยแจ้งเตือนเราเมื่อมีความพยายามทำให้ข้อมูลเสียหายแบบแยบยลได้
That's a good point about real-time detection. Emma, from your perspective on incident response, how quickly could we identify and contain such an event without that specific control?
เรื่องการตรวจจับแบบเรียลไทม์เป็นประเด็นที่ดีครับ เอ็มมา ในมุมมองด้านการรับมือเหตุการณ์ของคุณ เราจะตรวจพบและควบคุมเหตุการณ์แบบนี้ได้เร็วแค่ไหน หากไม่มีมาตรการควบคุมดังกล่าว

Without it, our detection would rely on daily integrity checks, meaning potential data corruption could go unnoticed for up to 24 hours. Containment would then be a race against time to restore from a clean backup, which adds significant recovery time objectives.
หากไม่มีระบบนี้ เราจะต้องอาศัยการตรวจสอบความถูกต้องครบถ้วนของข้อมูลวันละครั้งค่ะ นั่นหมายความว่าข้อมูลที่อาจเสียหายอาจไม่ถูกสังเกตเห็นนานถึง 24 ชั่วโมง จากนั้นการควบคุมสถานการณ์ก็จะกลายเป็นการแข่งกับเวลาเพื่อกู้คืนข้อมูลจากข้อมูลสำรองที่สะอาด ซึ่งทำให้ต้องใช้เวลาในการกู้คืนเพิ่มขึ้นมากค่ะ
So, effectively, the existing controls bring down the likelihood, but the impact remains critical, and the recovery time is still too high. We need to explore implementing that real-time anomaly detection, perhaps as a top priority.
สรุปคือ มาตรการควบคุมที่มีอยู่ช่วยลดโอกาสที่จะเกิด แต่ผลกระทบยังคงร้ายแรง และเวลาในการกู้คืนก็ยังนานเกินไป เราควรพิจารณานำระบบตรวจจับความผิดปกติแบบเรียลไทม์มาใช้ อาจจัดให้เป็นเรื่องสำคัญอันดับต้น ๆ เลยครับ
Agreed. Let's assign an action item to Mia and Jack to research potential vendors or in-house solutions for real-time anomaly detection. We'll need a cost-benefit analysis and a proposal for our next meeting. Thanks, everyone.
เห็นด้วยครับ มอบหมายงานให้มีอากับแจ็กไปค้นหาผู้ให้บริการหรือโซลูชันที่พัฒนาขึ้นเองสำหรับการตรวจจับความผิดปกติแบบเรียลไทม์นะครับ เราต้องมีการวิเคราะห์ต้นทุนและผลประโยชน์ พร้อมข้อเสนอสำหรับการประชุมครั้งหน้า ขอบคุณทุกคนครับ
คำศัพท์10
- vulnerabilitiesจุดอ่อน
Weak points or weaknesses in a system that can be attacked or exploited. In security, we use this to talk about potential dangers in technology like cloud systems.
หมายถึงจุดบกพร่องหรือจุดอ่อนในระบบที่อาจถูกโจมตีหรือนำไปใช้ประโยชน์ได้ ในด้านความปลอดภัย คำนี้ใช้พูดถึงอันตรายที่อาจเกิดขึ้นกับเทคโนโลยี เช่น ระบบคลาวด์
- data integrityความถูกต้องครบถ้วนของข้อมูล
The quality of data being accurate, complete, and unchanged. It's important in risk management to ensure information isn't damaged or altered without permission.
หมายถึงคุณภาพของข้อมูลที่ถูกต้อง ครบถ้วน และไม่ถูกเปลี่ยนแปลง ในการจัดการความเสี่ยง สิ่งนี้สำคัญเพื่อให้แน่ใจว่าข้อมูลจะไม่เสียหายหรือถูกแก้ไขโดยไม่ได้รับอนุญาต
- unauthorized accessการเข้าถึงโดยไม่ได้รับอนุญาต
Gaining entry to a system or data without permission. This is a common risk in cybersecurity discussions.
หมายถึงการเข้าถึงระบบหรือข้อมูลโดยไม่ได้รับอนุญาต เป็นความเสี่ยงที่พบได้บ่อยในการพูดคุยเรื่องความปลอดภัยทางไซเบอร์
- mitigateบรรเทา
To reduce the severity or risk of something harmful. In meetings, we say this when discussing ways to lessen dangers, like using controls.
หมายถึงลดความรุนแรงหรือความเสี่ยงของสิ่งที่เป็นอันตราย ในการประชุม เราใช้คำนี้เมื่อพูดถึงวิธีลดอันตราย เช่น การใช้มาตรการควบคุม
- encryptionการเข้ารหัส
A method to protect data by converting it into a code that can't be read without a key. It's a key tool in security to keep information safe.
วิธีปกป้องข้อมูลโดยแปลงให้เป็นรหัสที่อ่านไม่ได้หากไม่มีคีย์ เป็นเครื่องมือสำคัญด้านความปลอดภัยที่ช่วยรักษาข้อมูลให้ปลอดภัย
- anomaly detectionการตรวจจับความผิดปกติ
The process of identifying unusual patterns or activities that might indicate a problem, like in data streams for security monitoring.
กระบวนการค้นหารูปแบบหรือกิจกรรมที่ผิดปกติซึ่งอาจบ่งชี้ว่ามีปัญหา เช่น การตรวจสอบกระแสข้อมูลเพื่อเฝ้าระวังความปลอดภัย
- containmentการควบคุมสถานการณ์
The action of stopping or limiting the spread of a problem, such as isolating a security breach to prevent further damage.
การหยุดหรือจำกัดไม่ให้ปัญหาแพร่กระจาย เช่น แยกเหตุละเมิดความปลอดภัยออกจากระบบเพื่อป้องกันความเสียหายเพิ่มเติม
- recovery time objectivesเป้าหมายระยะเวลาในการกู้คืน
The target time set to restore normal operations after an incident. In risk talks, this helps plan how quickly to get back to normal.
ระยะเวลาเป้าหมายที่กำหนดไว้สำหรับการทำให้การดำเนินงานกลับสู่ภาวะปกติหลังเกิดเหตุ ในการพูดคุยเรื่องความเสี่ยง สิ่งนี้ช่วยวางแผนว่าจะกลับสู่ภาวะปกติได้เร็วแค่ไหน
- action itemงานที่ต้องดำเนินการ
A specific task assigned to someone in a meeting to follow up on. It's useful in professional settings to track responsibilities.
งานเฉพาะที่มอบหมายให้ใครบางคนในที่ประชุมไปดำเนินการต่อ เป็นสิ่งที่มีประโยชน์ในที่ทำงาน เพราะช่วยติดตามความรับผิดชอบได้
- cost-benefit analysisการวิเคราะห์ต้นทุนและผลประโยชน์
A comparison of the costs and benefits of a decision or project. In business meetings, this helps decide if something is worth doing.
การเปรียบเทียบต้นทุนกับผลประโยชน์ของการตัดสินใจหรือโครงการ ในการประชุมทางธุรกิจ วิธีนี้ช่วยให้ตัดสินใจได้ว่าคุ้มค่าที่จะทำหรือไม่
ประโยคสำคัญ8
- 1
Alright team, let's kick off this risk assessment meeting.
เอาละทุกคน เรามาเริ่มการประชุมประเมินความเสี่ยงกันเลย
This is a common way to start a professional meeting. 'Kick off' means to begin something energetically. Use it to gather attention and set the agenda; it's informal yet professional for team settings.
นี่เป็นวิธีเริ่มการประชุมในที่ทำงานที่ใช้กันทั่วไป 'Kick off' หมายถึงเริ่มต้นบางสิ่งอย่างกระตือรือร้น ใช้เรียกความสนใจและเริ่มเข้าสู่วาระการประชุมได้ ฟังดูเป็นกันเองแต่ยังเหมาะกับการประชุมในทีม
- 2
Our primary goal today is to revisit the potential vulnerabilities of our new cloud infrastructure.
เป้าหมายหลักของเราวันนี้คือทบทวนจุดอ่อนที่อาจเกิดขึ้นในโครงสร้างพื้นฐานคลาวด์ใหม่ของเรา
This sentence states the main purpose clearly. 'Revisit' means to look at something again, and 'primary goal' emphasizes importance. Useful for agendas in meetings; note the infinitive 'to revisit' after 'is'.
ประโยคนี้ระบุวัตถุประสงค์หลักอย่างชัดเจน 'Revisit' หมายถึงกลับมาพิจารณาบางสิ่งอีกครั้ง ส่วน 'primary goal' เน้นย้ำถึงเป้าหมายที่สำคัญ ใช้พูดถึงวาระการประชุมได้ดี และสังเกตว่าหลัง 'is' ใช้รูป infinitive 'to revisit'
- 3
Based on our analysis, the most significant risk is unauthorized access leading to data corruption or loss.
จากการวิเคราะห์ของเรา ความเสี่ยงที่สำคัญที่สุดคือการเข้าถึงโดยไม่ได้รับอนุญาต ซึ่งอาจทำให้ข้อมูลเสียหายหรือสูญหายได้
This explains a key finding with cause and effect ('leading to'). 'Based on' introduces evidence. Great for reports or discussions; it uses present simple for general facts about risks.
ประโยคนี้อธิบายข้อค้นพบสำคัญโดยแสดงเหตุและผลผ่าน 'leading to' ส่วน 'Based on' ใช้เกริ่นถึงหลักฐาน เหมาะสำหรับรายงานหรือการอภิปราย และใช้ present simple เพื่อกล่าวถึงข้อเท็จจริงทั่วไปเกี่ยวกับความเสี่ยง
- 4
We're looking at a likelihood of 'moderate' and a potential impact of 'critical' if it occurs.
เราประเมินโอกาสที่จะเกิดไว้ที่ระดับ 'ปานกลาง' และผลกระทบที่อาจเกิดขึ้นไว้ที่ระดับ 'ร้ายแรง' หากเกิดเหตุขึ้น
This describes risk levels using quotes for terms. 'Looking at' means considering. Helpful in assessments; conditional 'if it occurs' shows hypothetical impact, useful for planning.
ประโยคนี้อธิบายระดับความเสี่ยงโดยใส่คำศัพท์ไว้ในเครื่องหมายอัญประกาศ 'Looking at' หมายถึงกำลังพิจารณา เหมาะสำหรับการประเมินความเสี่ยง ส่วน 'if it occurs' เป็นเงื่อนไขสมมุติที่แสดงผลกระทบหากเกิดเหตุขึ้น จึงมีประโยชน์ต่อการวางแผน
- 5
What existing controls do we have in place to mitigate this?
ตอนนี้เรามีมาตรการควบคุมอะไรอยู่บ้างเพื่อบรรเทาความเสี่ยงนี้
A question to probe current measures. 'In place' means already implemented. Use in meetings to discuss solutions; it's a yes/no question with infinitive purpose 'to mitigate'.
นี่เป็นคำถามเพื่อสอบถามมาตรการที่ใช้อยู่ในปัจจุบัน 'In place' หมายถึงมีการนำมาใช้แล้ว ใช้ในการประชุมเพื่อพูดคุยถึงแนวทางแก้ไขได้ เป็นคำถามที่ตอบได้ว่าใช่หรือไม่ใช่ และใช้ infinitive 'to mitigate' เพื่อบอกจุดประสงค์
- 6
Without it, our detection would rely on daily integrity checks.
หากไม่มีระบบนี้ เราจะต้องอาศัยการตรวจสอบความถูกต้องครบถ้วนของข้อมูลวันละครั้ง
This contrasts scenarios with 'without it' for conditionals. 'Rely on' means depend on. Useful for explaining consequences; conditional 'would rely' shows hypothetical situations.
ประโยคนี้เปรียบเทียบสถานการณ์ด้วย 'without it' ซึ่งใช้ในประโยคเงื่อนไข 'Rely on' หมายถึงพึ่งพา ใช้อธิบายผลที่ตามมาได้ โดย 'would rely' แสดงสถานการณ์สมมุติ
- 7
We need to explore implementing that real-time anomaly detection, perhaps as a top priority.
เราควรพิจารณานำระบบตรวจจับความผิดปกติแบบเรียลไทม์มาใช้ อาจจัดให้เป็นเรื่องสำคัญอันดับต้น ๆ
Suggests action with 'need to' for necessity and 'perhaps' for suggestion. 'Top priority' means most important. Good for proposing next steps; gerund 'implementing' after 'explore'.
ประโยคนี้เสนอแนวทางด้วย 'need to' เพื่อแสดงความจำเป็น และ 'perhaps' เพื่อเสนอแนะ 'Top priority' หมายถึงสิ่งที่สำคัญที่สุด เหมาะสำหรับเสนอขั้นตอนถัดไป และหลัง 'explore' ใช้รูป gerund 'implementing'
- 8
Let's assign an action item to Mia and Jack to research potential vendors.
มอบหมายงานให้มีอากับแจ็กไปค้นหาผู้ให้บริการที่อาจเหมาะสม
Proposes task assignment with 'let's' for group agreement. Infinitive 'to research' shows purpose. Essential in meetings for follow-up; use to delegate responsibilities clearly.
ประโยคนี้เสนอการมอบหมายงานโดยใช้ 'let's' เพื่อชวนให้ทุกคนเห็นชอบ รูป infinitive 'to research' แสดงจุดประสงค์ เป็นสำนวนสำคัญสำหรับติดตามงานในการประชุม และใช้มอบหมายความรับผิดชอบให้ชัดเจน