Risk Assessment Meeting
ঝুঁকি মূল্যায়ন সভা
A team of security analysts conducts a detailed meeting to identify, analyze, and evaluate potential risks to the organization's assets. They discuss likelihood, impact, and existing controls, often using a risk matrix.
নিরাপত্তা বিশ্লেষকদের একটি দল প্রতিষ্ঠানের সম্পদের সম্ভাব্য ঝুঁকি শনাক্ত, বিশ্লেষণ ও মূল্যায়ন করতে বিস্তারিত সভা করে। তারা ঝুঁকির সম্ভাবনা, প্রভাব এবং বিদ্যমান নিয়ন্ত্রণব্যবস্থা নিয়ে আলোচনা করে; এ কাজে প্রায়ই ঝুঁকি ম্যাট্রিক্স ব্যবহার করা হয়।
সংলাপ8
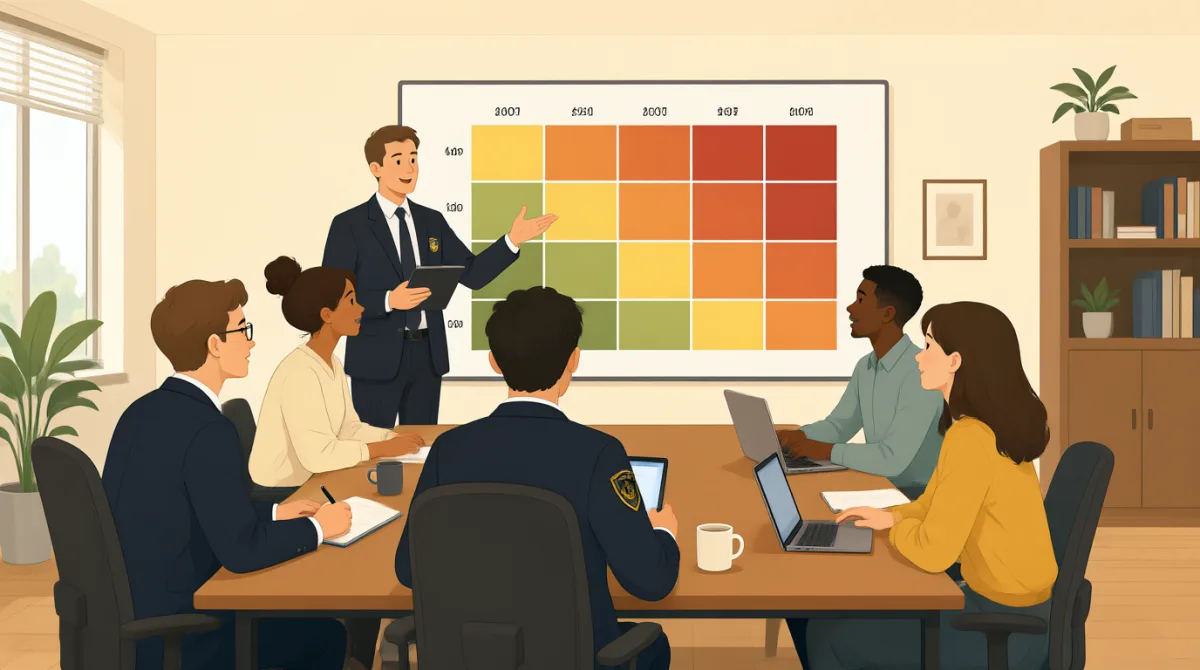

Alright team, let's kick off this risk assessment meeting. Our primary goal today is to revisit the potential vulnerabilities of our new cloud infrastructure, particularly concerning data integrity. Mia, could you start us off with your findings?
ঠিক আছে, সবাই, ঝুঁকি মূল্যায়নের এই সভা শুরু করা যাক। আজ আমাদের প্রধান লক্ষ্য হলো নতুন ক্লাউড অবকাঠামোর সম্ভাব্য দুর্বলতাগুলো আবার পর্যালোচনা করা, বিশেষ করে তথ্যের অখণ্ডতা নিয়ে। মিয়া, তুমি কি তোমার ফলাফল দিয়ে শুরু করবে?

Certainly, David. Based on our analysis, the most significant risk is unauthorized access leading to data corruption or loss. We're looking at a likelihood of 'moderate' and a potential impact of 'critical' if it occurs.
অবশ্যই, ডেভিড। আমাদের বিশ্লেষণ অনুযায়ী, সবচেয়ে বড় ঝুঁকি হলো অনুমতি ছাড়া প্রবেশ, যার ফলে তথ্য নষ্ট বা হারিয়ে যেতে পারে। এর সম্ভাবনা ‘মাঝারি’ এবং ঘটলে সম্ভাব্য প্রভাব ‘সংকটজনক’ বলে আমরা বিবেচনা করছি।

Moderate likelihood, critical impact… that puts it squarely in the 'high risk' category on our matrix. What existing controls do we have in place to mitigate this, Mia?
সম্ভাবনা মাঝারি, প্রভাব সংকটজনক… তাহলে আমাদের ম্যাট্রিক্সে এটা স্পষ্টভাবেই ‘উচ্চ ঝুঁকি’ বিভাগে পড়ে। মিয়া, এটা কমানোর জন্য আমাদের কী কী নিয়ন্ত্রণব্যবস্থা আছে?
Currently, we have robust encryption and multi-factor authentication. However, the gap identified is the lack of real-time anomaly detection within the data streams themselves, which could alert us to subtle corruption attempts.
এখন আমাদের শক্তিশালী এনক্রিপশন এবং বহু-ধাপ যাচাইকরণ আছে। তবে যে ঘাটতিটা ধরা পড়েছে, তা হলো ডেটা স্ট্রিমের মধ্যে রিয়েল-টাইমে অস্বাভাবিকতা শনাক্ত করার ব্যবস্থা নেই। এমন ব্যবস্থা থাকলে সূক্ষ্মভাবে তথ্য নষ্ট করার চেষ্টা সম্পর্কে আমাদের সতর্ক করতে পারত।
That's a good point about real-time detection. Emma, from your perspective on incident response, how quickly could we identify and contain such an event without that specific control?
রিয়েল-টাইমে শনাক্ত করার বিষয়টা ভালো বলেছ। এমা, ঘটনার প্রতিক্রিয়া নিয়ে তোমার অভিজ্ঞতা থেকে বলো—এই নির্দিষ্ট নিয়ন্ত্রণব্যবস্থা ছাড়া এমন ঘটনা আমরা কত দ্রুত শনাক্ত করে নিয়ন্ত্রণে আনতে পারব?

Without it, our detection would rely on daily integrity checks, meaning potential data corruption could go unnoticed for up to 24 hours. Containment would then be a race against time to restore from a clean backup, which adds significant recovery time objectives.
এটা না থাকলে আমাদের শনাক্তকরণ প্রতিদিনের অখণ্ডতা যাচাইয়ের ওপর নির্ভর করবে। অর্থাৎ, সম্ভাব্য তথ্যবিকৃতি ২৪ ঘণ্টা পর্যন্ত আমাদের নজরে না-ও আসতে পারে। এরপর পরিষ্কার ব্যাকআপ থেকে পুনরুদ্ধার করতে হবে, আর সময়ের সঙ্গে পাল্লা দিয়ে পরিস্থিতি সামলাতে হবে। এতে পুনরুদ্ধারের জন্য নির্ধারিত সময়সীমাও উল্লেখযোগ্যভাবে বেড়ে যাবে।
So, effectively, the existing controls bring down the likelihood, but the impact remains critical, and the recovery time is still too high. We need to explore implementing that real-time anomaly detection, perhaps as a top priority.
তাহলে মোটের ওপর, বিদ্যমান নিয়ন্ত্রণব্যবস্থাগুলো ঝুঁকির সম্ভাবনা কমায়, কিন্তু প্রভাব এখনো সংকটজনক, আর পুনরুদ্ধারে লাগা সময়ও অনেক বেশি। আমাদের রিয়েল-টাইমে অস্বাভাবিকতা শনাক্ত করার ব্যবস্থা চালু করার বিষয়টি খতিয়ে দেখা দরকার—হয়তো এটাকে সর্বোচ্চ অগ্রাধিকার দেওয়া উচিত।
Agreed. Let's assign an action item to Mia and Jack to research potential vendors or in-house solutions for real-time anomaly detection. We'll need a cost-benefit analysis and a proposal for our next meeting. Thanks, everyone.
একমত। মিয়া আর জ্যাককে একটি করণীয় দিই—রিয়েল-টাইমে অস্বাভাবিকতা শনাক্ত করার জন্য সম্ভাব্য সরবরাহকারী বা নিজেদের তৈরি সমাধান খুঁজে দেখতে। পরের সভার জন্য আমাদের খরচ-সুবিধা বিশ্লেষণ এবং একটি প্রস্তাব লাগবে। সবাইকে ধন্যবাদ।
শব্দভান্ডার10
- vulnerabilitiesদুর্বলতাগুলো
Weak points or weaknesses in a system that can be attacked or exploited. In security, we use this to talk about potential dangers in technology like cloud systems.
কোনো ব্যবস্থার এমন দুর্বল দিক, যেগুলোতে আক্রমণ করা বা সুযোগ নেওয়া যায়। নিরাপত্তার ক্ষেত্রে ক্লাউড ব্যবস্থার মতো প্রযুক্তিতে সম্ভাব্য বিপদ বোঝাতে এই শব্দটি ব্যবহার করা হয়।
- data integrityতথ্যের অখণ্ডতা
The quality of data being accurate, complete, and unchanged. It's important in risk management to ensure information isn't damaged or altered without permission.
তথ্য নির্ভুল, সম্পূর্ণ এবং অপরিবর্তিত থাকার গুণ। ঝুঁকি ব্যবস্থাপনায় এটি নিশ্চিত করা জরুরি, যাতে অনুমতি ছাড়া তথ্য নষ্ট বা পরিবর্তিত না হয়।
- unauthorized accessঅনুমতি ছাড়া প্রবেশ
Gaining entry to a system or data without permission. This is a common risk in cybersecurity discussions.
অনুমতি ছাড়াই কোনো ব্যবস্থা বা তথ্যে প্রবেশ করা। সাইবার নিরাপত্তা নিয়ে আলোচনায় এটি একটি সাধারণ ঝুঁকি।
- mitigateকমিয়ে আনা
To reduce the severity or risk of something harmful. In meetings, we say this when discussing ways to lessen dangers, like using controls.
কোনো ক্ষতিকর বিষয়ের তীব্রতা বা ঝুঁকি কমানো। বিপদ কমানোর উপায়, যেমন নিয়ন্ত্রণব্যবস্থা, নিয়ে আলোচনার সময় এই শব্দটি ব্যবহার করা হয়।
- encryptionএনক্রিপশন
A method to protect data by converting it into a code that can't be read without a key. It's a key tool in security to keep information safe.
তথ্যকে এমন সাংকেতিক রূপে বদলে সুরক্ষিত রাখার পদ্ধতি, যা চাবি ছাড়া পড়া যায় না। তথ্য নিরাপদ রাখার জন্য এটি নিরাপত্তার একটি গুরুত্বপূর্ণ উপায়।
- anomaly detectionঅস্বাভাবিকতা শনাক্তকরণ
The process of identifying unusual patterns or activities that might indicate a problem, like in data streams for security monitoring.
সমস্যার ইঙ্গিত দিতে পারে—এমন অস্বাভাবিক ধরন বা কার্যকলাপ খুঁজে বের করার প্রক্রিয়া। নিরাপত্তা পর্যবেক্ষণের জন্য ডেটা স্ট্রিমে এ ধরনের শনাক্তকরণ করা হয়।
- containmentনিয়ন্ত্রণে আনা
The action of stopping or limiting the spread of a problem, such as isolating a security breach to prevent further damage.
কোনো সমস্যা ছড়িয়ে পড়া থামানো বা সীমিত করার কাজ। যেমন, আরও ক্ষতি ঠেকাতে নিরাপত্তা লঙ্ঘনের ঘটনাটি আলাদা করে রাখা।
- recovery time objectivesপুনরুদ্ধারের লক্ষ্যমাত্রা সময়
The target time set to restore normal operations after an incident. In risk talks, this helps plan how quickly to get back to normal.
কোনো ঘটনার পর স্বাভাবিক কার্যক্রম ফিরিয়ে আনতে যে লক্ষ্যমাত্রা সময় নির্ধারণ করা হয়। ঝুঁকি নিয়ে আলোচনায় এটি স্বাভাবিক অবস্থায় কত দ্রুত ফেরা যাবে, তা পরিকল্পনা করতে সাহায্য করে।
- action itemকরণীয় কাজ
A specific task assigned to someone in a meeting to follow up on. It's useful in professional settings to track responsibilities.
সভায় কাউকে দেওয়া নির্দিষ্ট কাজ, যা পরে সম্পন্ন করতে হবে। পেশাগত পরিবেশে দায়িত্বের অগ্রগতি নজরে রাখতে এটি কাজে লাগে।
- cost-benefit analysisখরচ-সুবিধা বিশ্লেষণ
A comparison of the costs and benefits of a decision or project. In business meetings, this helps decide if something is worth doing.
কোনো সিদ্ধান্ত বা প্রকল্পের খরচ ও সুবিধার তুলনা। ব্যবসায়িক সভায় কোনো উদ্যোগ নেওয়া লাভজনক হবে কি না, তা বুঝতে এটি সাহায্য করে।
গুরুত্বপূর্ণ বাক্য8
- 1
Alright team, let's kick off this risk assessment meeting.
ঠিক আছে, সবাই, ঝুঁকি মূল্যায়নের এই সভা শুরু করা যাক।
This is a common way to start a professional meeting. 'Kick off' means to begin something energetically. Use it to gather attention and set the agenda; it's informal yet professional for team settings.
পেশাগত সভা শুরু করার এটি একটি প্রচলিত উপায়। 'Kick off' মানে উদ্যম নিয়ে কোনো কিছু শুরু করা। সবার মনোযোগ আকর্ষণ করে আলোচ্য বিষয় জানাতে এটি ব্যবহার করো; দলের মধ্যে এটি অনানুষ্ঠানিক হলেও পেশাগতভাবে মানানসই।
- 2
Our primary goal today is to revisit the potential vulnerabilities of our new cloud infrastructure.
আজ আমাদের প্রধান লক্ষ্য হলো নতুন ক্লাউড অবকাঠামোর সম্ভাব্য দুর্বলতাগুলো আবার পর্যালোচনা করা।
This sentence states the main purpose clearly. 'Revisit' means to look at something again, and 'primary goal' emphasizes importance. Useful for agendas in meetings; note the infinitive 'to revisit' after 'is'.
এই বাক্যে সভার মূল উদ্দেশ্য পরিষ্কারভাবে বলা হয়েছে। 'Revisit' মানে কোনো কিছু আবার দেখা বা পর্যালোচনা করা, আর 'primary goal' দিয়ে এর গুরুত্ব বোঝানো হয়। সভার আলোচ্য বিষয় জানাতে এটি কাজে লাগে। খেয়াল করো, 'is'-এর পরে 'to revisit' ব্যবহার হয়েছে।
- 3
Based on our analysis, the most significant risk is unauthorized access leading to data corruption or loss.
আমাদের বিশ্লেষণ অনুযায়ী, সবচেয়ে বড় ঝুঁকি হলো অনুমতি ছাড়া প্রবেশ, যার ফলে তথ্য নষ্ট বা হারিয়ে যেতে পারে।
This explains a key finding with cause and effect ('leading to'). 'Based on' introduces evidence. Great for reports or discussions; it uses present simple for general facts about risks.
এখানে একটি গুরুত্বপূর্ণ ফলাফল এবং তার কারণ-পরিণতি ('leading to') বোঝানো হয়েছে। 'Based on' দিয়ে প্রমাণ বা বিশ্লেষণের ভিত্তি জানানো হয়। প্রতিবেদন বা আলোচনায় এটি কাজে লাগে; ঝুঁকি সম্পর্কে সাধারণ তথ্য জানাতে এখানে বর্তমান কাল ব্যবহার করা হয়েছে।
- 4
We're looking at a likelihood of 'moderate' and a potential impact of 'critical' if it occurs.
এর সম্ভাবনা ‘মাঝারি’ এবং ঘটলে সম্ভাব্য প্রভাব ‘সংকটজনক’ বলে আমরা বিবেচনা করছি।
This describes risk levels using quotes for terms. 'Looking at' means considering. Helpful in assessments; conditional 'if it occurs' shows hypothetical impact, useful for planning.
এখানে ঝুঁকির মাত্রা বোঝাতে উদ্ধৃতিচিহ্নসহ শব্দ ব্যবহার করা হয়েছে। 'Looking at' মানে বিবেচনা করা। ঝুঁকি মূল্যায়নে এটি কাজে লাগে; 'if it occurs' দিয়ে কোনো ঘটনা ঘটলে তার সম্ভাব্য প্রভাব বোঝানো হয়েছে, যা পরিকল্পনার জন্য উপযোগী।
- 5
What existing controls do we have in place to mitigate this?
এটা কমানোর জন্য আমাদের কী কী বিদ্যমান নিয়ন্ত্রণব্যবস্থা আছে?
A question to probe current measures. 'In place' means already implemented. Use in meetings to discuss solutions; it's a yes/no question with infinitive purpose 'to mitigate'.
বর্তমানে কী কী ব্যবস্থা আছে, তা জানতে এই প্রশ্ন করা হয়। 'In place' মানে ইতিমধ্যে চালু বা বাস্তবায়িত। সমাধান নিয়ে সভায় আলোচনা করতে এটি ব্যবহার করো। এটি হ্যাঁ-না ধরনের প্রশ্ন, আর 'to mitigate' দিয়ে উদ্দেশ্য বোঝানো হয়েছে।
- 6
Without it, our detection would rely on daily integrity checks.
এটা না থাকলে আমাদের শনাক্তকরণ প্রতিদিনের অখণ্ডতা যাচাইয়ের ওপর নির্ভর করবে।
This contrasts scenarios with 'without it' for conditionals. 'Rely on' means depend on. Useful for explaining consequences; conditional 'would rely' shows hypothetical situations.
'Without it' দিয়ে শর্তসাপেক্ষে দুটি পরিস্থিতির পার্থক্য বোঝানো হয়েছে। 'Rely on' মানে নির্ভর করা। কোনো কিছুর পরিণতি ব্যাখ্যা করতে এটি কাজে লাগে; 'would rely' দিয়ে কাল্পনিক পরিস্থিতি বোঝানো হয়েছে।
- 7
We need to explore implementing that real-time anomaly detection, perhaps as a top priority.
আমাদের রিয়েল-টাইমে অস্বাভাবিকতা শনাক্ত করার ব্যবস্থা চালু করার বিষয়টি খতিয়ে দেখা দরকার—হয়তো এটাকে সর্বোচ্চ অগ্রাধিকার দেওয়া উচিত।
Suggests action with 'need to' for necessity and 'perhaps' for suggestion. 'Top priority' means most important. Good for proposing next steps; gerund 'implementing' after 'explore'.
'Need to' দিয়ে প্রয়োজনীয়তা, আর 'perhaps' দিয়ে প্রস্তাব বা সম্ভাবনা বোঝানো হয়েছে। 'Top priority' মানে সবচেয়ে গুরুত্বপূর্ণ কাজ। পরবর্তী পদক্ষেপের প্রস্তাব দিতে এটি ভালোভাবে কাজে লাগে। 'Explore'-এর পরে কাজ বা প্রক্রিয়া বোঝাতে 'implementing' ব্যবহার করা হয়েছে।
- 8
Let's assign an action item to Mia and Jack to research potential vendors.
চলো, সম্ভাব্য সরবরাহকারীদের খুঁজে দেখার জন্য মিয়া আর জ্যাককে একটি করণীয় কাজ দিই।
Proposes task assignment with 'let's' for group agreement. Infinitive 'to research' shows purpose. Essential in meetings for follow-up; use to delegate responsibilities clearly.
'Let's' দিয়ে সবাই মিলে কোনো কাজের প্রস্তাব দেওয়া হয়েছে। 'To research' দিয়ে কাজটির উদ্দেশ্য বোঝানো হয়েছে। সভায় পরবর্তী পদক্ষেপ ঠিক করতে এবং দায়িত্ব স্পষ্টভাবে ভাগ করে দিতে এই বাক্যরীতি খুব দরকারি।