Risk Assessment Meeting
जोखिम आकलन बैठक
A team of security analysts conducts a detailed meeting to identify, analyze, and evaluate potential risks to the organization's assets. They discuss likelihood, impact, and existing controls, often using a risk matrix.
सुरक्षा विश्लेषकों की एक टीम संगठन की परिसंपत्तियों के संभावित जोखिमों की पहचान करने, उनका विश्लेषण करने और आकलन करने के लिए विस्तृत बैठक करती है। वे जोखिम होने की संभावना, उसके प्रभाव और मौजूदा नियंत्रण उपायों पर चर्चा करते हैं और अक्सर जोखिम मैट्रिक्स का उपयोग करते हैं।
संवाद8
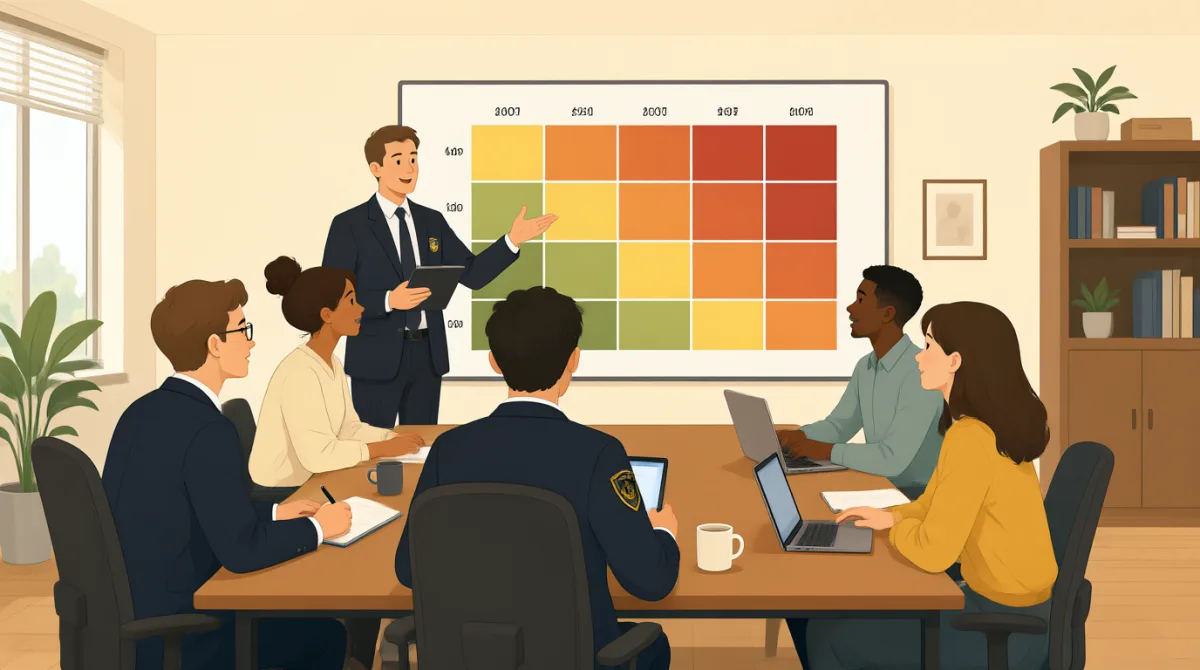

Alright team, let's kick off this risk assessment meeting. Our primary goal today is to revisit the potential vulnerabilities of our new cloud infrastructure, particularly concerning data integrity. Mia, could you start us off with your findings?
ठीक है, टीम, आइए जोखिम आकलन की यह बैठक शुरू करें। आज हमारा मुख्य लक्ष्य नए क्लाउड ढाँचे की संभावित कमजोरियों की फिर से समीक्षा करना है, खासकर डेटा की अखंडता से जुड़ी कमजोरियों की। मिया, क्या आप अपने निष्कर्षों से शुरुआत कर सकती हैं?

Certainly, David. Based on our analysis, the most significant risk is unauthorized access leading to data corruption or loss. We're looking at a likelihood of 'moderate' and a potential impact of 'critical' if it occurs.
बिल्कुल, डेविड। हमारे विश्लेषण के अनुसार, सबसे बड़ा जोखिम बिना अनुमति के पहुँच हासिल करना है, जिससे डेटा खराब हो सकता है या खो सकता है। हमारी निगाह में इसकी संभावना 'मध्यम' है और ऐसा होने पर इसका संभावित प्रभाव 'गंभीर' होगा।

Moderate likelihood, critical impact… that puts it squarely in the 'high risk' category on our matrix. What existing controls do we have in place to mitigate this, Mia?
संभावना मध्यम, प्रभाव गंभीर… इसका मतलब है कि हमारे मैट्रिक्स में यह साफ़ तौर पर 'उच्च जोखिम' की श्रेणी में आता है। मिया, इसे कम करने के लिए हमारे पास अभी कौन-से नियंत्रण उपाय हैं?
Currently, we have robust encryption and multi-factor authentication. However, the gap identified is the lack of real-time anomaly detection within the data streams themselves, which could alert us to subtle corruption attempts.
अभी हमारे पास मजबूत एन्क्रिप्शन और बहु-कारक प्रमाणीकरण है। लेकिन हमने जो कमी पहचानी है, वह है डेटा स्ट्रीम में ही रीयल-टाइम विसंगति पहचान की सुविधा का न होना। यह डेटा में छेड़छाड़ की सूक्ष्म कोशिशों के बारे में हमें सचेत कर सकती है।
That's a good point about real-time detection. Emma, from your perspective on incident response, how quickly could we identify and contain such an event without that specific control?
रीयल-टाइम पहचान की बात सही है। एमा, घटना-प्रतिक्रिया के अपने अनुभव से बताइए, उस खास नियंत्रण उपाय के बिना हम ऐसी घटना की पहचान करके उसे कितनी जल्दी रोक सकते हैं?

Without it, our detection would rely on daily integrity checks, meaning potential data corruption could go unnoticed for up to 24 hours. Containment would then be a race against time to restore from a clean backup, which adds significant recovery time objectives.
उसके बिना, हमें रोज़ाना की अखंडता जाँच पर निर्भर रहना होगा। यानी डेटा में हुई संभावित गड़बड़ी 24 घंटे तक पकड़ में नहीं आएगी। फिर उसे रोकने के लिए साफ़ बैकअप से डेटा बहाल करने की होड़ होगी, जिससे ठीक होने में लगने वाला समय काफी बढ़ जाएगा।
So, effectively, the existing controls bring down the likelihood, but the impact remains critical, and the recovery time is still too high. We need to explore implementing that real-time anomaly detection, perhaps as a top priority.
तो कुल मिलाकर, मौजूदा नियंत्रण उपाय जोखिम होने की संभावना तो घटाते हैं, लेकिन प्रभाव गंभीर ही रहता है और बहाली में लगने वाला समय भी अब तक बहुत ज़्यादा है। हमें रीयल-टाइम विसंगति पहचान लागू करने पर विचार करना चाहिए—शायद इसे सबसे ऊपर की प्राथमिकता के तौर पर।
Agreed. Let's assign an action item to Mia and Jack to research potential vendors or in-house solutions for real-time anomaly detection. We'll need a cost-benefit analysis and a proposal for our next meeting. Thanks, everyone.
सहमत हूँ। मिया और जैक को यह पता लगाने का काम सौंपते हैं कि रीयल-टाइम विसंगति पहचान के लिए संभावित विक्रेता कौन हैं या क्या हम अपना समाधान तैयार कर सकते हैं। अगली बैठक के लिए हमें लागत-लाभ विश्लेषण और एक प्रस्ताव चाहिए होगा। सभी का धन्यवाद।
शब्दावली10
- vulnerabilitiesकमजोरियाँ
Weak points or weaknesses in a system that can be attacked or exploited. In security, we use this to talk about potential dangers in technology like cloud systems.
किसी सिस्टम के ऐसे कमजोर पहलू जिन पर हमला किया जा सकता है या जिनका फ़ायदा उठाया जा सकता है। सुरक्षा के संदर्भ में, इस शब्द का इस्तेमाल क्लाउड सिस्टम जैसी तकनीकों के संभावित खतरों की बात करते समय होता है।
- data integrityडेटा की अखंडता
The quality of data being accurate, complete, and unchanged. It's important in risk management to ensure information isn't damaged or altered without permission.
डेटा का सही, पूरा और बिना बदलाव के होना। जोखिम प्रबंधन में यह सुनिश्चित करना ज़रूरी है कि जानकारी को नुकसान न पहुँचे और उसमें बिना अनुमति बदलाव न किया जाए।
- unauthorized accessबिना अनुमति के पहुँच
Gaining entry to a system or data without permission. This is a common risk in cybersecurity discussions.
बिना अनुमति के किसी सिस्टम या डेटा तक पहुँच हासिल करना। साइबर सुरक्षा की चर्चाओं में यह एक आम जोखिम है।
- mitigateकम करना
To reduce the severity or risk of something harmful. In meetings, we say this when discussing ways to lessen dangers, like using controls.
किसी हानिकारक चीज़ की गंभीरता या जोखिम घटाना। बैठकों में इसका इस्तेमाल खतरे कम करने के तरीकों, जैसे नियंत्रण उपायों, पर चर्चा करते समय किया जाता है।
- encryptionएन्क्रिप्शन
A method to protect data by converting it into a code that can't be read without a key. It's a key tool in security to keep information safe.
डेटा को ऐसे कूट में बदलकर सुरक्षित करने का तरीका, जिसे कुंजी के बिना पढ़ा नहीं जा सकता। जानकारी की सुरक्षा के लिए यह एक अहम उपाय है।
- anomaly detectionविसंगति की पहचान
The process of identifying unusual patterns or activities that might indicate a problem, like in data streams for security monitoring.
ऐसे असामान्य पैटर्न या गतिविधियों की पहचान करने की प्रक्रिया जो किसी समस्या का संकेत दे सकती हैं। सुरक्षा निगरानी के लिए डेटा स्ट्रीम में ऐसी पहचान की जा सकती है।
- containmentरोकथाम
The action of stopping or limiting the spread of a problem, such as isolating a security breach to prevent further damage.
किसी समस्या को फैलने से रोकने या उसका फैलाव सीमित करने की कार्रवाई। उदाहरण के लिए, आगे नुकसान रोकने के लिए सुरक्षा उल्लंघन को अलग-थलग करना।
- recovery time objectivesबहाली के लिए लक्षित समय
The target time set to restore normal operations after an incident. In risk talks, this helps plan how quickly to get back to normal.
किसी घटना के बाद सामान्य कामकाज बहाल करने के लिए तय किया गया लक्ष्य समय। जोखिम पर चर्चा में इससे यह योजना बनाने में मदद मिलती है कि सामान्य स्थिति में कितनी जल्दी लौटा जा सकता है।
- action itemकार्रवाई का काम
A specific task assigned to someone in a meeting to follow up on. It's useful in professional settings to track responsibilities.
बैठक में किसी व्यक्ति को आगे की कार्रवाई के लिए सौंपा गया खास काम। पेशेवर माहौल में इससे ज़िम्मेदारियों पर नज़र रखने में मदद मिलती है।
- cost-benefit analysisलागत-लाभ विश्लेषण
A comparison of the costs and benefits of a decision or project. In business meetings, this helps decide if something is worth doing.
किसी फैसले या परियोजना की लागत और उससे मिलने वाले लाभों की तुलना। कारोबारी बैठकों में इससे तय करने में मदद मिलती है कि किसी काम को करना फ़ायदेमंद है या नहीं।
मुख्य वाक्य8
- 1
Alright team, let's kick off this risk assessment meeting.
ठीक है, टीम, आइए जोखिम आकलन की यह बैठक शुरू करें।
This is a common way to start a professional meeting. 'Kick off' means to begin something energetically. Use it to gather attention and set the agenda; it's informal yet professional for team settings.
पेशेवर बैठक शुरू करने का यह एक आम तरीका है। 'Kick off' का मतलब है किसी काम को जोश के साथ शुरू करना। सबका ध्यान खींचने और बैठक का एजेंडा तय करने के लिए इसका इस्तेमाल करें। टीम के बीच यह अनौपचारिक, लेकिन पेशेवर लगता है।
- 2
Our primary goal today is to revisit the potential vulnerabilities of our new cloud infrastructure.
आज हमारा मुख्य लक्ष्य नए क्लाउड ढाँचे की संभावित कमजोरियों की फिर से समीक्षा करना है।
This sentence states the main purpose clearly. 'Revisit' means to look at something again, and 'primary goal' emphasizes importance. Useful for agendas in meetings; note the infinitive 'to revisit' after 'is'.
इस वाक्य में बैठक का मुख्य उद्देश्य साफ़ बताया गया है। 'Revisit' का मतलब है किसी चीज़ पर दोबारा विचार करना, जबकि 'primary goal' उसके सबसे अहम उद्देश्य पर ज़ोर देता है। बैठक का एजेंडा बताते समय यह उपयोगी है। ध्यान दें कि 'is' के बाद 'to revisit' आया है।
- 3
Based on our analysis, the most significant risk is unauthorized access leading to data corruption or loss.
हमारे विश्लेषण के अनुसार, सबसे बड़ा जोखिम बिना अनुमति के पहुँच हासिल करना है, जिससे डेटा खराब हो सकता है या खो सकता है।
This explains a key finding with cause and effect ('leading to'). 'Based on' introduces evidence. Great for reports or discussions; it uses present simple for general facts about risks.
यह वाक्य कारण और परिणाम बताकर एक अहम निष्कर्ष समझाता है। 'Based on' का इस्तेमाल किसी सबूत या जानकारी के आधार को बताने के लिए होता है। रिपोर्ट और चर्चाओं में यह उपयोगी है। जोखिमों से जुड़े सामान्य तथ्यों के लिए इसमें वर्तमान सरल काल का इस्तेमाल हुआ है।
- 4
We're looking at a likelihood of 'moderate' and a potential impact of 'critical' if it occurs.
हमारी निगाह में इसकी संभावना 'मध्यम' है और ऐसा होने पर इसका संभावित प्रभाव 'गंभीर' होगा।
This describes risk levels using quotes for terms. 'Looking at' means considering. Helpful in assessments; conditional 'if it occurs' shows hypothetical impact, useful for planning.
यह वाक्य जोखिम के स्तर बताता है और उनके लिए उद्धरण चिह्नों में दिए गए शब्दों का इस्तेमाल करता है। 'Looking at' का मतलब है किसी बात पर विचार करना। आकलन में यह काम आता है। 'If it occurs' की शर्त से संभावित प्रभाव का पता चलता है, जो योजना बनाने में उपयोगी है।
- 5
What existing controls do we have in place to mitigate this?
इसे कम करने के लिए हमारे पास अभी कौन-से नियंत्रण उपाय हैं?
A question to probe current measures. 'In place' means already implemented. Use in meetings to discuss solutions; it's a yes/no question with infinitive purpose 'to mitigate'.
यह सवाल मौजूदा उपायों के बारे में जानकारी माँगता है। 'In place' का मतलब है कि कोई उपाय पहले से लागू है। समाधानों पर चर्चा के लिए बैठक में इसका इस्तेमाल करें। इसमें 'to mitigate' यह बताता है कि उपाय किस उद्देश्य से हैं।
- 6
Without it, our detection would rely on daily integrity checks.
उसके बिना, हमें रोज़ाना की अखंडता जाँच पर निर्भर रहना होगा।
This contrasts scenarios with 'without it' for conditionals. 'Rely on' means depend on. Useful for explaining consequences; conditional 'would rely' shows hypothetical situations.
यह वाक्य 'without it' के ज़रिए दो स्थितियों की तुलना करता है। 'Rely on' का मतलब है किसी चीज़ पर निर्भर रहना। नतीजे समझाने में यह उपयोगी है। 'Would rely' का इस्तेमाल एक काल्पनिक स्थिति बताने के लिए हुआ है।
- 7
We need to explore implementing that real-time anomaly detection, perhaps as a top priority.
हमें रीयल-टाइम विसंगति पहचान लागू करने पर विचार करना चाहिए—शायद इसे सबसे ऊपर की प्राथमिकता के तौर पर।
Suggests action with 'need to' for necessity and 'perhaps' for suggestion. 'Top priority' means most important. Good for proposing next steps; gerund 'implementing' after 'explore'.
'Need to' से ज़रूरत या अनिवार्यता और 'perhaps' से सुझाव का भाव आता है। 'Top priority' का मतलब है सबसे ज़्यादा अहमियत वाला काम। अगले कदम सुझाते समय यह वाक्य उपयोगी है। 'Explore' के बाद 'implementing' का इस्तेमाल किया गया है।
- 8
Let's assign an action item to Mia and Jack to research potential vendors.
आइए, मिया और जैक को संभावित विक्रेताओं के बारे में पता लगाने का काम सौंपें।
Proposes task assignment with 'let's' for group agreement. Infinitive 'to research' shows purpose. Essential in meetings for follow-up; use to delegate responsibilities clearly.
'Let's' का इस्तेमाल समूह की सहमति से किसी काम का प्रस्ताव रखने के लिए होता है। 'To research' से काम का उद्देश्य पता चलता है। बैठक में आगे की कार्रवाई तय करने और ज़िम्मेदारियाँ साफ़-साफ़ सौंपने के लिए यह उपयोगी है।